
#DirectAdmin
Two Critical PHP RCE Flaws (php2shell): Patch Today
CVE-2026-109618 and CVE-2026-109619 are PHP RCE vulnerabilities with a CVSS score of 9.2 and public exploits already available. They affect every machine using PHP to handle web requests. The patched versions are 8.5.12, 8.4.27, 8.3.36, and 8.2.35. This note covers version checks, updates on Debian, RHEL, DirectAdmin, Docker, and Windows, and temporary settings while waiting for patches.
Writing to DirectAdmin Through Panel Forms When the API Only Reads
Notes on letting a back-office app create and edit hosting packages in DirectAdmin when the official CMD_API only provides read operations, requiring POST requests directly to control panel forms, with verification rules that prohibit regex and two layers of kill switches disabled by default.
tinker Sends Mail but the Web Can't — proc_open Disabled in FPM
Sending mail from tinker works perfectly, but submitting the actual form sends nothing, and the mail log has no entries — because CLI and PHP-FPM are not the same PHP environment. Includes a working SMTP AUTH configuration for DirectAdmin hosting and the From rule you must get right.
Site Not Updating After Deploy — Clear All Five Cache Layers
The files are uploaded, but the site still shows the old version, even after Ctrl+F5 — because five cache layers sit between the files on disk and what people see, and each needs a different clearing method. This article covers the sequence I use regularly, along with the trap that leaves the site stuck on 500 after clearing the view cache.
route:cache Turns Every GET into 405 — The Sub-path Trap
Deployment finished, I ran optimize as the guides suggested, and every page returned 405 Method Not Allowed even though route:list confirmed the routes were correct — a route cache that breaks only on certain servers, how to isolate it in 30 seconds, and three other issues I found while deploying an app under a sub-path.
Static on DirectAdmin: GET Returns 404 but HEAD Returns 200
I uploaded a static site to public_html and could not open it. Small files worked, large files returned 404, but HEAD returned 200 for every file. The cause was Laravel's .htaccess at the docroot, funneling everything into the front controller. This article covers the diagnosis and three ways out.
Laravel Behind a Proxy Sees 127.0.0.1 — Silent Form, No Error
A contact form on DirectAdmin says the sender is not human, sends no mail, and leaves every log silent — the cause is Laravel behind nginx-to-apache seeing $request->ip() as 127.0.0.1, failing the bot check and returning before the mail is sent, with an explanation of why TrustProxies must not use '*'
My Firewall Permanently Banned Googlebot and Hid Sites from Search
I investigated why sites disappeared from search results and found Googlebot in my own firewall's permanent ban list. 408 of 500 entries came from the counter tallying WAF false positives. How I lifted the bans, wrote a script to fetch official bot IP ranges into the ignore list daily, and dealt with a grep trap and the side effects of blocking entire countries.
MariaDB on defaults — a 128M buffer pool on a 55 GB RAM server
A 16 core server with 55 GB RAM and an SSD, but MariaDB still had the default 128 MB buffer pool. The result was 50 million disk reads in 5 days. The full before-and-after settings, service name and config path traps on DirectAdmin/Debian, rollback steps, and another 500 MyISAM tables waiting for conversion.
AI Crawler Overloads ?add-to-cart= — Block It Without Hurting SEO
Server load triggered an email alert. The logs showed that 84% of the day's traffic came from one AI crawler following add-to-cart links for every product. I added layers of protection with robots.txt, rel=nofollow and nginx limit_req while keeping all product pages indexable.

Stolen Mailbox Password Sent 1,786 Spam Emails Unseen by CSF/LFD
A real case of a stolen mailbox password used to send 50-75 spam emails a day, below a limit of 200, for 4 straight weeks without a single response from CSF/LFD/BFM because they only count failed authentication attempts, with the decisive question of whether an account was compromised or merely under attack, exim forensic commands, and a blocklist removal playbook
Set DirectAdmin Admin Backup Cron from the CLI Without the Panel
CMD_ADMIN_BACKUP takes five steps to set up a cron job, but DirectAdmin actually just appends one line to backup_crons.list and lets dataskq pick it up. Here is how to write directly to the file from the CLI, including common traps with when=now, base64, and append_to_path.

nginx heap overflow spans 15 years—version checks aren't enough
CVE-2026-42533 affects nginx versions 0.9.6 through 1.31.2, spanning 15 years, but actual exposure depends on the config, not the version. The problem is that news reports describe narrower conditions than the real ones. Checking against those reports can return "safe" even when the config still meets the conditions.

Read-only Debian shared-host security audit — avoid banning yourself
Audit the security of a Debian server running DirectAdmin in read-only mode first — but the first trap is that scan traffic itself triggers CSF's brute-force rules and gets your own IP banned. This article lays out a safe audit sequence + areas to check in 2024-2026

Mail Checks Ban the Whole Office—Fixing It with Login Auto-Whitelist
Real mail clients behave exactly like bots — office machines keep retrying old passwords until CSF bans the whole office. This article covers an auto-whitelist system that watches for successful logins + Thai GeoIP, then grants a temporary allow for 24 hours, along with 5 pitfalls I learned the hard way.
Per-user Redis on shared hosting—and the maxmemory bug that hung sites
Designing one Redis instance per user on shared hosting with a systemd template + cgroup — and lessons from a maxmemory bug where setting it above the cgroup limit caused intermittent WooCommerce hangs, plus the 80% rule and a guard script to prevent recurrence
WordPress 500s, Empty debug.log — The Fatal Is in the Apache Log
WordPress returns 500 only on portfolio pages, but debug.log is empty — because the fatal error during theme rendering happens before WP logging is ready. The answer is in the apache error log (proxy_fcgi), along with a fix for a child theme with a stale template copied from an older parent version.
Lost the .com: Move to .net on DirectAdmin Without Data Loss
A .com domain expired and ended up with a domain squatter — how I moved the whole site (files/mail/DNS/SSL) to a new .net domain on DirectAdmin with a single CMD_CHANGE_DOMAIN command, plus 4 follow-up tasks that do not happen automatically
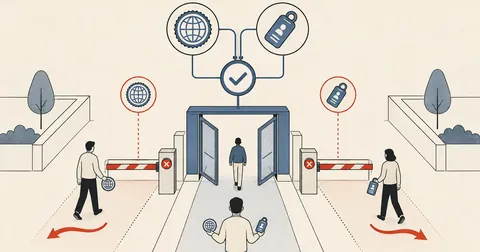
Auto-Unblock the Office in CSF with a Geo+Account Gate
A real case of a client office whose IP changes daily, with a ghost device using an old password that repeatedly gets the whole office blocked by CSF. How I automated unblocking with a narrow account+geo gate that lets the real office through while keeping foreign credential attacks blocked.
A Telegram Bot for DA Server Monitoring with a Small Blast Radius
A guide to setting up a Telegram bot as a lightweight control surface for monitoring a DirectAdmin server — read-only commands plus IP blocking/unblocking only, with no open ports, no added services, and a blast radius limited by least privilege at every layer
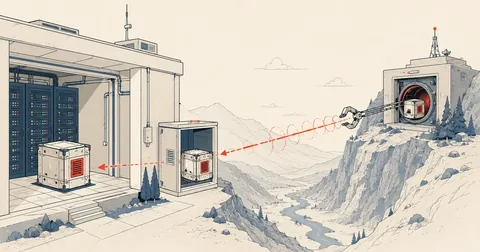
Off-Site Backups with Pull Architecture + rclone/rsync
Add off-site Layer 3 to complete 3-2-1 with pull architecture (the destination host fetches the data), rclone + rsync, and lessons from real pitfalls involving NAT, RSA host keys, cwRsync, and PID recycling.
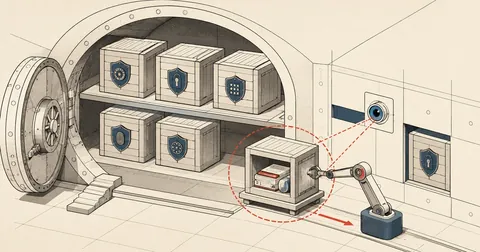
Rebuilding DirectAdmin Backups with NFS and POSIX ACL in Production
A record of rebuilding backups on a DirectAdmin server after migrating to a new machine — from FTP push that broke at three layers to an NFSv4 hard mount + POSIX ACL, with kernel-level lessons learned along the way.

Reading exim mainlog for Stuck Clients — Mail Forensics Part 1
How I read /var/log/exim/mainlog to distinguish an office machine using the wrong password from an attacker running a brute force attack, with the commands I use when customers need answers fast.
Tracing Dovecot IMAP/POP Failures on DirectAdmin and Keeping 90-Day Logs
A follow-up to Mail Forensics — trace IMAP/POP failures in /var/log/mail.log on DirectAdmin, distinguish stuck clients from attackers using cross-protocol ratios, and adjust logrotate to keep a full 90 days of logs instead of defaults that lose them within days
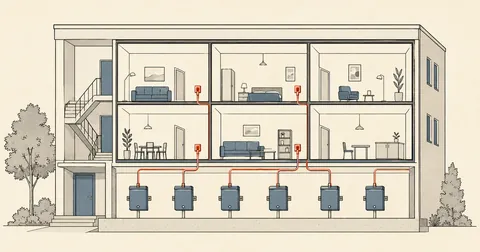
Per-User Redis on DirectAdmin Without Buying pro_pack
How to set up per-user Redis object cache on DirectAdmin shared hosting with a systemd template + unix socket + cgroup limit, using a custom provisioning script instead of the DA panel that requires a pro_pack license, with connection recipes for WordPress, Flarum, and Laravel
Tuning ModSecurity on DirectAdmin for Shared Hosting
The 4 additions I made beyond DA defaults — exclusions before CRS, a 1-hit credscan ban, a fix for the incorrect MODSEC_LOG path shipped by DA, and a self-heal cron to recover from rebuild overwrites
DirectAdmin from CentOS 7 to Debian 12 on Proxmox (Series Index)
Notes on migrating a DirectAdmin shared host from CentOS 7 (EOL) to Debian 12 on Proxmox, serving 80+ customers, split into 5 parts with an overview of the process and links to every part
DA Migration Finale — Security Fixes and Hardening After Stabilizing
Wrapping up the cross-distro DirectAdmin migration series with security work after the server stabilized — sudoers wildcard CVE, OpenSSL SECLEVEL, ModSec exclusions before CRS, a csfpost drop-in, and 5 layers that survive DA updates
Moving DA from CentOS 7 to Debian 12, Part 4 — Cutover and 17 Issues
The actual cutover, where the near-0 downtime plan fell apart because of the DA Legacy license and slow qcow2 reads, ended with 1 hour of downtime and 17 issues in quick succession after the switch — critical web stack outages, medium issues affecting subsets of services, and minor debugging notes.
DA Migration Part 3 — DirectAdmin + CustomBuild on Debian 12
Installing DirectAdmin through setup.sh, then assembling a stack with multiple PHP versions, MariaDB, ModSecurity, and rspamd using CustomBuild on a staging VM behind NAT, including pitfalls I ran into myself.
Moving DA to Debian 12, Part 2 — Switching Storage to a ZFS Mirror
Replace the three storage layers of mdadm RAID1 + ext4 + qcow2 with a single layer of ZFS mirror + raw zvol while the old VM stays online, by degrading RAID to a single disk.
DA CentOS 7 → Debian 12 on Proxmox Part 1 — NAT pre-stage
Preparing a new VM on an internal bridge with NAT while the old VM continues serving customers, reducing downtime when migrating DirectAdmin from CentOS 7 to Debian 12 on Proxmox.
CSF Auto-Unblock for Ghost Devices Amid Botnet Brute Force
A real case on a DA shared host where a ghost device in an office got the entire office blocked by CSF every morning. I explain a 4-layer auto-unblock setup that distinguishes office devices from a botnet without accidentally unblocking attackers.