
#CSF Firewall
Egress Firewall Breaks Domain Checks — Tests as root Pass
The domain order page reported every name as unavailable, even names I made up. The cause was an outbound DROP policy with port 43 missing from the allowed port list after an operating system migration. The trap was that tests as root passed every time. Testing must use the account that actually runs the app.
My Firewall Permanently Banned Googlebot and Hid Sites from Search
I investigated why sites disappeared from search results and found Googlebot in my own firewall's permanent ban list. 408 of 500 entries came from the counter tallying WAF false positives. How I lifted the bans, wrote a script to fetch official bot IP ranges into the ignore list daily, and dealt with a grep trap and the side effects of blocking entire countries.

Stolen Mailbox Password Sent 1,786 Spam Emails Unseen by CSF/LFD
A real case of a stolen mailbox password used to send 50-75 spam emails a day, below a limit of 200, for 4 straight weeks without a single response from CSF/LFD/BFM because they only count failed authentication attempts, with the decisive question of whether an account was compromised or merely under attack, exim forensic commands, and a blocklist removal playbook

Read-only Debian shared-host security audit — avoid banning yourself
Audit the security of a Debian server running DirectAdmin in read-only mode first — but the first trap is that scan traffic itself triggers CSF's brute-force rules and gets your own IP banned. This article lays out a safe audit sequence + areas to check in 2024-2026

Mail Checks Ban the Whole Office—Fixing It with Login Auto-Whitelist
Real mail clients behave exactly like bots — office machines keep retrying old passwords until CSF bans the whole office. This article covers an auto-whitelist system that watches for successful logins + Thai GeoIP, then grants a temporary allow for 24 hours, along with 5 pitfalls I learned the hard way.
Managing Linux Servers Safely with AI over SSH
How I actually use Claude to audit and fix Linux server security over SSH, from preparing my machine and storing secrets to hard rules before touching production
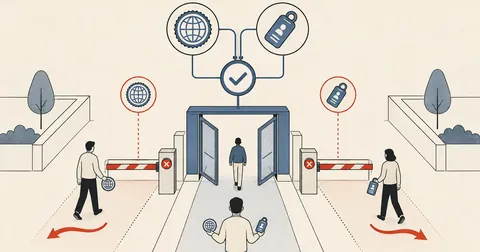
Auto-Unblock the Office in CSF with a Geo+Account Gate
A real case of a client office whose IP changes daily, with a ghost device using an old password that repeatedly gets the whole office blocked by CSF. How I automated unblocking with a narrow account+geo gate that lets the real office through while keeping foreign credential attacks blocked.
A Telegram Bot for DA Server Monitoring with a Small Blast Radius
A guide to setting up a Telegram bot as a lightweight control surface for monitoring a DirectAdmin server — read-only commands plus IP blocking/unblocking only, with no open ports, no added services, and a blast radius limited by least privilege at every layer
Rebuilding DirectAdmin Backups with NFS and POSIX ACL in Production
A record of rebuilding backups on a DirectAdmin server after migrating to a new machine — from FTP push that broke at three layers to an NFSv4 hard mount + POSIX ACL, with kernel-level lessons learned along the way.

Reading exim mainlog for Stuck Clients — Mail Forensics Part 1
How I read /var/log/exim/mainlog to distinguish an office machine using the wrong password from an attacker running a brute force attack, with the commands I use when customers need answers fast.
Tuning ModSecurity on DirectAdmin for Shared Hosting
The 4 additions I made beyond DA defaults — exclusions before CRS, a 1-hit credscan ban, a fix for the incorrect MODSEC_LOG path shipped by DA, and a self-heal cron to recover from rebuild overwrites
DA Migration Finale — Security Fixes and Hardening After Stabilizing
Wrapping up the cross-distro DirectAdmin migration series with security work after the server stabilized — sudoers wildcard CVE, OpenSSL SECLEVEL, ModSec exclusions before CRS, a csfpost drop-in, and 5 layers that survive DA updates
Moving DA from CentOS 7 to Debian 12, Part 4 — Cutover and 17 Issues
The actual cutover, where the near-0 downtime plan fell apart because of the DA Legacy license and slow qcow2 reads, ended with 1 hour of downtime and 17 issues in quick succession after the switch — critical web stack outages, medium issues affecting subsets of services, and minor debugging notes.
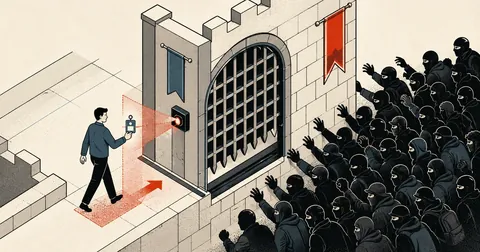
CSF Auto-Unblock for Ghost Devices Amid Botnet Brute Force
A real case on a DA shared host where a ghost device in an office got the entire office blocked by CSF every morning. I explain a 4-layer auto-unblock setup that distinguishes office devices from a botnet without accidentally unblocking attackers.