
#Hardening
Secrets Set to 600, but 0644 Logs Go Offsite Every Night
The .env is encrypted and permissions are locked down on every secret file, but customer data still leaks off the machine every night through something nobody classifies as confidential: logs that every account on the machine can read, bundled into backups uploaded to object storage. Here is how I stop it at the source by logging only result codes.
Egress Firewall Breaks Domain Checks — Tests as root Pass
The domain order page reported every name as unavailable, even names I made up. The cause was an outbound DROP policy with port 43 missing from the allowed port list after an operating system migration. The trap was that tests as root passed every time. Testing must use the account that actually runs the app.
Web vs. Worker — mkdir 0700 Disables Inherited ACL Permissions
One app runs as two users, with php-fpm handling web requests and a separate account running the queue. Even with default ACLs fully configured, they still cannot write to each other's directories. The cause is mkdir with mode 0700, which sets a mask that wipes out the effective ACL permissions, plus a deletion trap that requires permissions on the directory, not the file.
Encrypt Secrets in .env and Decrypt Them When Config Loads
How to store passwords and API keys as ciphertext in Laravel's .env and have config decrypt them on load, using a single helper that detects encrypted values, plus the APP_KEY mismatch across environments that can bring everything down if you get it wrong.

Auditing a Deployed Laravel Site — 3 Layers in Priority Order
After deploying Laravel to production, check security in 3 layers — probe externally for exposed endpoints, check files/permissions on the server, then grep for vulnerabilities in the code. This article provides commands and P0-P2 priorities for deciding what to fix first.

nginx heap overflow spans 15 years—version checks aren't enough
CVE-2026-42533 affects nginx versions 0.9.6 through 1.31.2, spanning 15 years, but actual exposure depends on the config, not the version. The problem is that news reports describe narrower conditions than the real ones. Checking against those reports can return "safe" even when the config still meets the conditions.

Read-only Debian shared-host security audit — avoid banning yourself
Audit the security of a Debian server running DirectAdmin in read-only mode first — but the first trap is that scan traffic itself triggers CSF's brute-force rules and gets your own IP banned. This article lays out a safe audit sequence + areas to check in 2024-2026
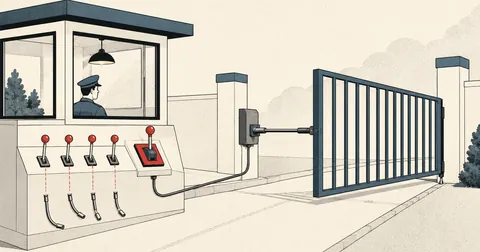
libmodsecurity3 + nginx — only ctl:ruleEngine exclusions work
ModSecurity v3 (libmodsecurity3) + nginx + OWASP CRS — the ctl:ruleRemoveById taught in the guides does nothing and fails silently. This article covers what I found after trying every approach: ctl:ruleEngine works, scoped with a Host+URI chained rule, and the exclusion file must load before CRS.
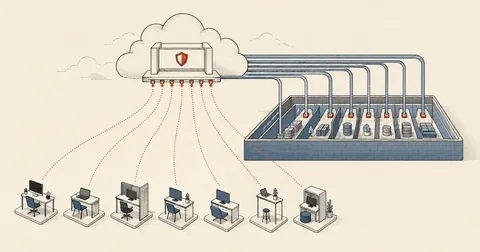
LAN Access for a Team of 7 Without Open Ports: Cloudflare Zero Trust
A team of 7 needs RDP access to machines on the LAN without opening any ports to the internet — the Cloudflare Zero Trust architecture (WARP + cloudflared), with 3 lessons from implementation: a forgotten IdP setup, Gateway defaults that allow everything, and the default-deny rule people forget most often
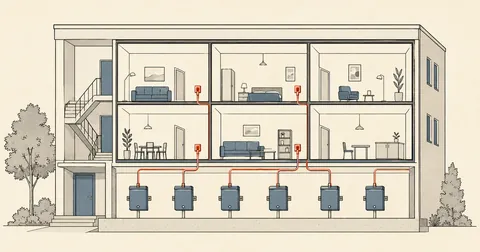
Per-User Redis on DirectAdmin Without Buying pro_pack
How to set up per-user Redis object cache on DirectAdmin shared hosting with a systemd template + unix socket + cgroup limit, using a custom provisioning script instead of the DA panel that requires a pro_pack license, with connection recipes for WordPress, Flarum, and Laravel
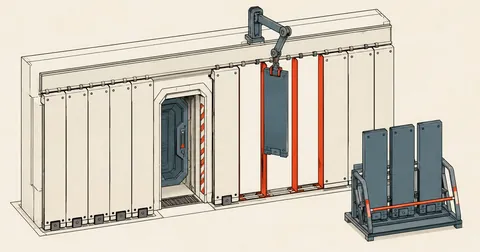
Tuning ModSecurity on DirectAdmin for Shared Hosting
The 4 additions I made beyond DA defaults — exclusions before CRS, a 1-hit credscan ban, a fix for the incorrect MODSEC_LOG path shipped by DA, and a self-heal cron to recover from rebuild overwrites
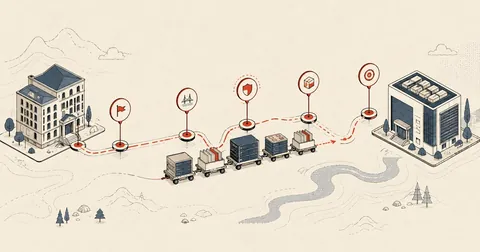
DirectAdmin from CentOS 7 to Debian 12 on Proxmox (Series Index)
Notes on migrating a DirectAdmin shared host from CentOS 7 (EOL) to Debian 12 on Proxmox, serving 80+ customers, split into 5 parts with an overview of the process and links to every part
DA Migration Finale — Security Fixes and Hardening After Stabilizing
Wrapping up the cross-distro DirectAdmin migration series with security work after the server stabilized — sudoers wildcard CVE, OpenSSL SECLEVEL, ModSec exclusions before CRS, a csfpost drop-in, and 5 layers that survive DA updates