Ingesting Mail Without Disrupting Someone Else's Mailbox
The mailbox the app fetches from is one people actually use every day — fetching with UNSEEN silently misses mail when the owner reads it on their phone before cron runs. The right approach is UID SEARCH paired with UIDVALIDITY and BODY.PEEK, with deduplication handled on our side.
tinker Sends Mail but the Web Can't — proc_open Disabled in FPM
Sending mail from tinker works perfectly, but submitting the actual form sends nothing, and the mail log has no entries — because CLI and PHP-FPM are not the same PHP environment. Includes a working SMTP AUTH configuration for DirectAdmin hosting and the From rule you must get right.

Mailbox Compromised or Just Password Guessing? Prove It First
Telling a customer their account has been compromised is an allegation that needs decisive evidence first. This article covers what counts as decisive evidence, two cases with opposite outcomes, and the case I nearly reported incorrectly.
Laravel Behind a Proxy Sees 127.0.0.1 — Silent Form, No Error
A contact form on DirectAdmin says the sender is not human, sends no mail, and leaves every log silent — the cause is Laravel behind nginx-to-apache seeing $request->ip() as 127.0.0.1, failing the bot check and returning before the mail is sent, with an explanation of why TrustProxies must not use '*'

Stolen Mailbox Password Sent 1,786 Spam Emails Unseen by CSF/LFD
A real case of a stolen mailbox password used to send 50-75 spam emails a day, below a limit of 200, for 4 straight weeks without a single response from CSF/LFD/BFM because they only count failed authentication attempts, with the decisive question of whether an account was compromised or merely under attack, exim forensic commands, and a blocklist removal playbook
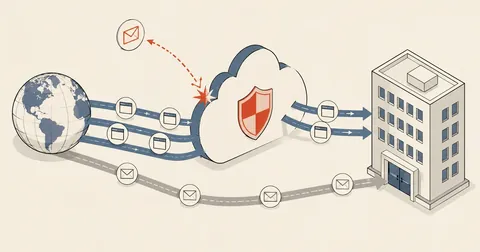
Mail Stopped After Moving to Cloudflare — Proxied Mail Records
After adding a domain to Cloudflare and pointing DNS at the host, incoming mail suddenly stops — the most common cause I see is leaving mail/smtp/pop records proxied (orange cloud), even though Cloudflare's proxy only handles HTTP/S. This article covers which records must be grey + token/SSL pitfalls.

Mail Checks Ban the Whole Office—Fixing It with Login Auto-Whitelist
Real mail clients behave exactly like bots — office machines keep retrying old passwords until CSF bans the whole office. This article covers an auto-whitelist system that watches for successful logins + Thai GeoIP, then grants a temporary allow for 24 hours, along with 5 pitfalls I learned the hard way.
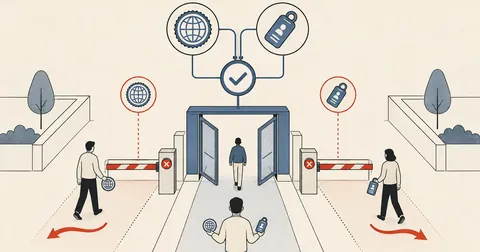
Auto-Unblock the Office in CSF with a Geo+Account Gate
A real case of a client office whose IP changes daily, with a ghost device using an old password that repeatedly gets the whole office blocked by CSF. How I automated unblocking with a narrow account+geo gate that lets the real office through while keeping foreign credential attacks blocked.

Reading exim mainlog for Stuck Clients — Mail Forensics Part 1
How I read /var/log/exim/mainlog to distinguish an office machine using the wrong password from an attacker running a brute force attack, with the commands I use when customers need answers fast.
Tracing Dovecot IMAP/POP Failures on DirectAdmin and Keeping 90-Day Logs
A follow-up to Mail Forensics — trace IMAP/POP failures in /var/log/mail.log on DirectAdmin, distinguish stuck clients from attackers using cross-protocol ratios, and adjust logrotate to keep a full 90 days of logs instead of defaults that lose them within days